Authenticate 2026: Day 1 Recap
By FIDO Staff
Authenticate 2026, the FIDO Alliance’s flagship conference, kicked off day one as the ‘first mile’ of authentication in an era where agentic AI is a growing concern across all sectors.
The first day was loaded with sessions on how organizations are advancing passkey adoption, considering identity verification and dealing with the agentic AI onslaught.
Passkeys and Agentic AI
Developer Office Hours opened FIDO Authenticate 2026 with host Megan Shamas, Senior Director of Product Marketing at OneSpan and Market Strategy alongside Tim Cappalli, Senior Architect, Identity Standards and Okta and Matthew Miller, Director of Product Management, Cybersecurity at OneSpan. The session covered an eclectic combination of topics with AI being a primary concern.
Cappalli set the tone early with a warning about the new reality of passkey development in the AI era.
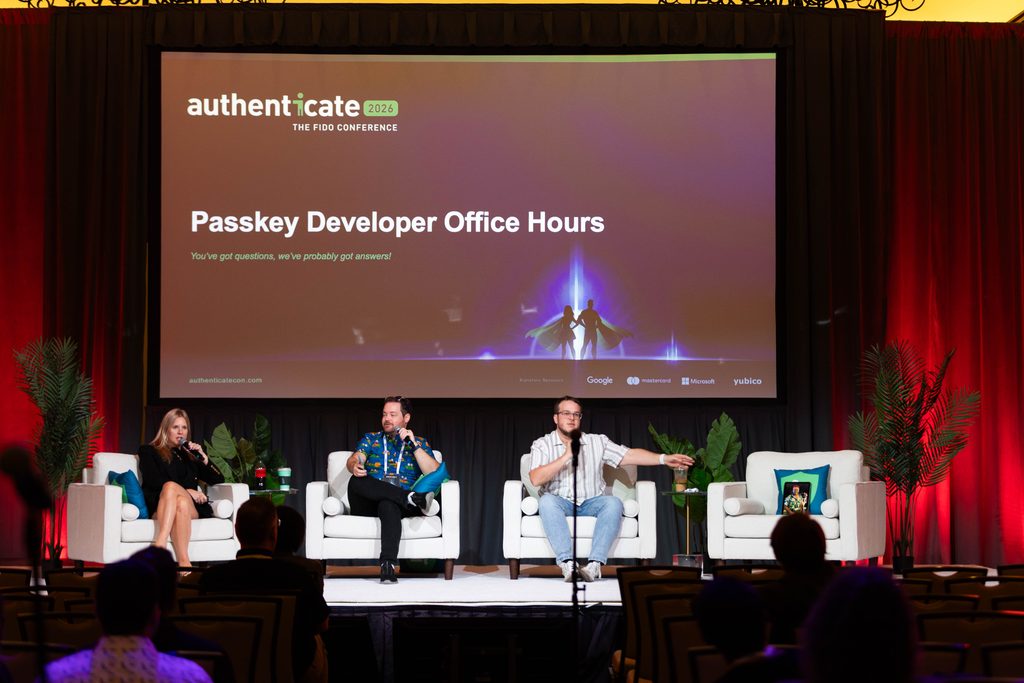
“Agents are dangerously good at implementing passkeys,” Cappalli said. The catch is that they miss important details, so docs and sites like passkeys.dev now need to speak to agents as well as people.
During the Q&A, a question came up on device-bound versus synced passkeys for the workforce. Shamas pushed back on the idea that synced passkeys are not fit for the enterprise.
“There are definitely very big companies that have rolled sync passkeys for their entire workforces with success,” she said.
Grading Passkey Implementations
How good is a passkey implementation? Today the answer is often going to be somewhat arbitrary but an emerging effort at FIDO is going to provide some clarity to help grade passkey implementations.
In a morning panel session Mitchell Galavan, Senior UX & Product Designer at Google, James Hwang, Senior Product Designer at Microsoft and Judy Clare, Executive Director, Product Manager, Customer Identity & Authentication at JPMorgan Chase, detailed a 16-check rubric that lets any team grade its own rollout. The speakers are all also members of the FIDO UX Working Group, which led the development of the rubric.
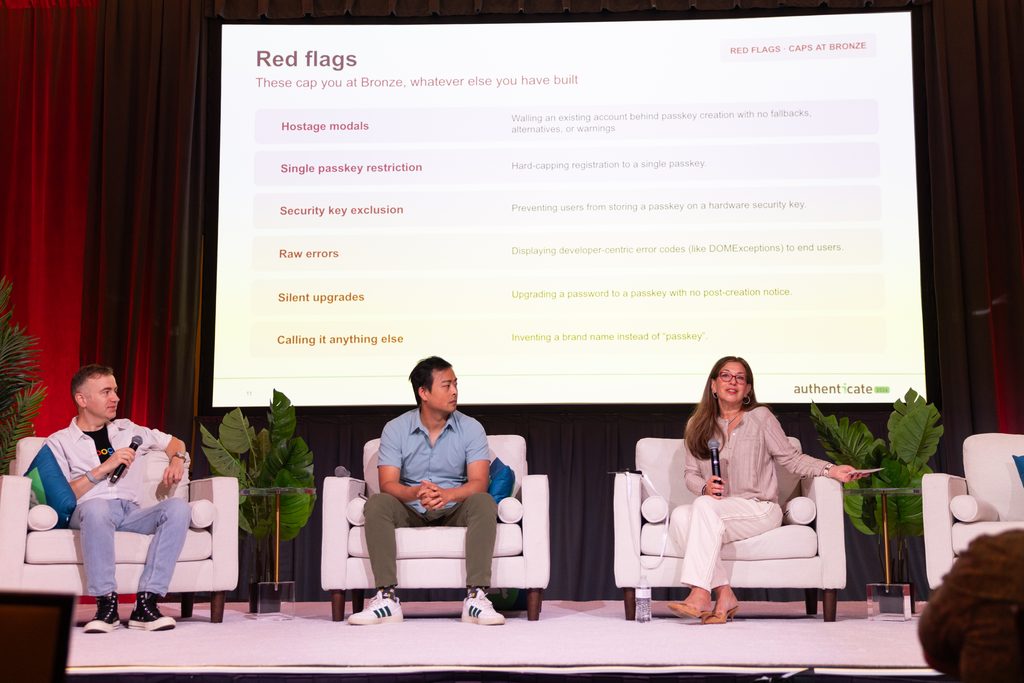
- Bronze. This is the required floor. It means a passkey home in settings, a visible fallback, support for multiple passkeys and one consistent name and icon.
- Silver. This is the launch target. It covers autofill, smart prompting for mobile and desktop, graceful errors and accessibility.
- Gold. This tier adds automatic passkey upgrades, Signal API syncing and recovery matched to your risk.
- Platinum. This is the bonus round. It asks for account hardening and related origins across domains.
Bronze and silver are the realistic goal for most teams, and gold and platinum are for growing past a solid launch.
Fundamentally it’s all about improving user experience and security.
“The goal is to make it easier and more secure for them to log in, not to block them,” Clare said.
Spotify: How to Design Authentication for 750m+ Users
Spotify is available around the world, works across all types of devices and users span every demographic. That ubiquity can be a challenge for authentication design.

“When I started at Spotify, everything I learned in university and my career before that went out of the window super super fast because, as a designer, you always start to pick a persona or someone specific to design for,” Quendoline Jansen, Senior Product Designer at Spotify said. “But what if you design for literally everyone?”
Laura de Bella, Engineering Manager at Spotify, said that it was clear that passwords needed to go away but when Spotify first had to prioritize between all the options to get rid of passwords, passkeys was not the obvious choice initially due to challenges with onboarding. That situation has now changed and Spotify is now on a path toward enabling passkeys across its diverse user base.
For passkeys, the team designs enrollment for the best moment. Its research shows that is about 10 seconds after login, or better still during an account recovery flow.
“It was really important for us to accept that passkeys are a year-long path, so we are not talking about a launch,” de Bella said. “We are talking about a plan. The shift needs to be gradual, and we understand that it needs to coexist with a lot of other methods.”
From Policy to Passkeys at eBay
How do you get thousands of employees to leave passwords behind? At eBay, the answer wasn’t a single mandate or another reminder email.
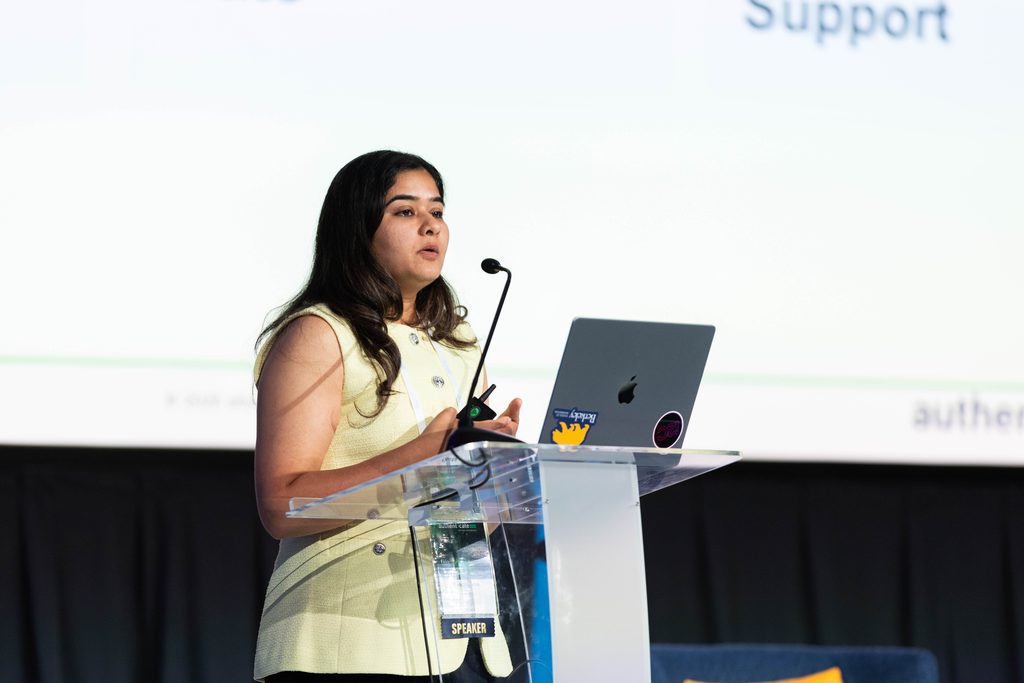
Tanu Kaushik, Senior Manager at eBay, described a staged rollout: first make FIDO an easy, voluntary option; then make it the preferred path, while building enrolment into new-hire and device-replacement journeys.
“FIDO alongside a password, was our phase one. You do not mandate marriage on the first date,” she said.
The adoption push was deliberate. eBay used targeted emails, leadership scorecards, office signage and clear privacy guidance to keep FIDO visible and address employee concerns. It also gave qualifying users a compelling perk: no routine password changes.
The results were dramatic with 73% reduction in login time and 81% fewer help desk incidents.
Kaushik had three key lessons:
- Treat is like a product lunch
- Governance before scale
- Plan for heterogeneity
“We are not deploying a policy. You are launching a product that nobody asks for, and everyone needs,” she said.

A Tale of Scaling Secure Login Across Singapore
Singapore’s national digital identity system SingPass is the digital front door for everyday life.
Samantha Li of GovTech Singapore explained how the service is adding device-bound passkeys to strengthen protection against phishing and scam-driven account takeovers.The team made passkeys feel approachable with clear setup guidance, a gentle pause while the passkey is saved, and an easy first login to try it out. They launched on iOS first, then expanded to Android after proving reliability.
So far, 1.15 million people have created passkeys, which now account for about 10% of logins. Li emphasized that adoption depends not just on strong technology, but on helping people feel confident using it.
“I believe that passkeys has successfully uplifted the login security of all Singaporeans,” Li said.
Keynotes: FIDOs Vision for the Future has an Identity
The day-one keynotes were kicked off by none other than Andrew Shikiar, Executive Director & CEO of the FIDO Alliance, who started by providing a visionary outlook on where authentication and identity will be in 2030. It’s a future that relies on trust.

“Let’s talk about the frontier between us and 2030, and the new frontier must be built upon a foundation of trust,” Shikiar said. “We believe the way people interact with services, both online and in person, will increasingly rely upon verified human identity.”
Shikiar tied the vision to three pieces of FIDO work.
Digital credentials. FIDO is building a baseline wallet certification profile that gives issuers, verifiers and wallet providers a common target. A new external advisory forum for issuers and regulators holds its first meeting in November.
Passkeys. More than 7 billion are now in use worldwide, and over a third of successful sign-ins use one. Those sign-ins are about three times faster, and more of them succeed. “Passkeys bring business value. Full stop,” Shikiar said.
Agentic payments. A working draft of the agentic payments specification is coming soon. It builds on Google’s AP2 and Mastercard’s Verifiable Intent. Shikiar called it probably the most active working area in the Alliance.
The keynote ended with a call to action.
“Let’s go build the foundation of trust together that will underpin the internet of the next decade,” Shikiar said.
Keynote: Google on the Role AI and Strong Authentication
Christiaan Brand, Principal Product Manager at Google, opened the second keynote with a simple question for the agentic era. When an AI agent sits at the keyboard, who just logged in?
Brand argued that relying parties now need to verify user intent, not just identity. Then he walked the room through three decades of authentication history, scoring each milestone against a short list of pillars that include a hardware root of trust, ease of use, public key cryptography and unique per-account credentials.
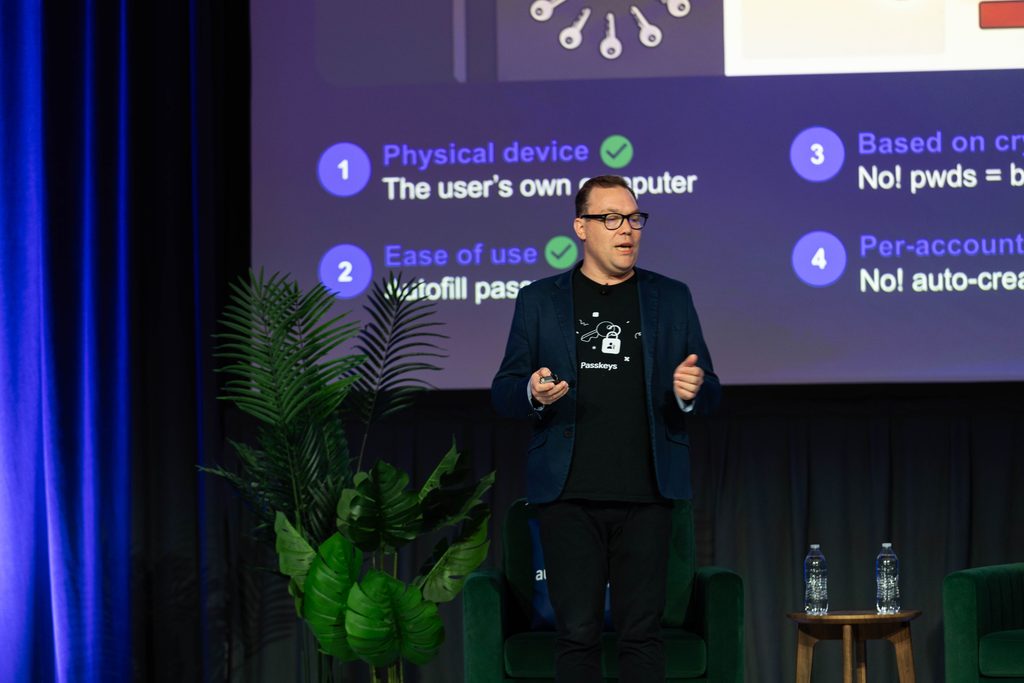
“Strong authentication is the linchpin of our agentic future,” Brand said.
Brand closed by pulling the pieces together. For the first time, he said, there is a clear end-to-end architecture for the human account lifecycle. Passkeys handle sign-in. Phishing-resistant phone numbers and later digital IDs close the recovery backdoor. Trust group keys give websites the provenance.
“Putting all of these pieces together really gives us something that we’ve never had in the history of the internet, a verifiable cryptographic root of trust for human user across the entire lifecycle of an account,” he said.
Keynote: Chase’s Identity Chief on Passkeys, Credentials and the Agent Problem
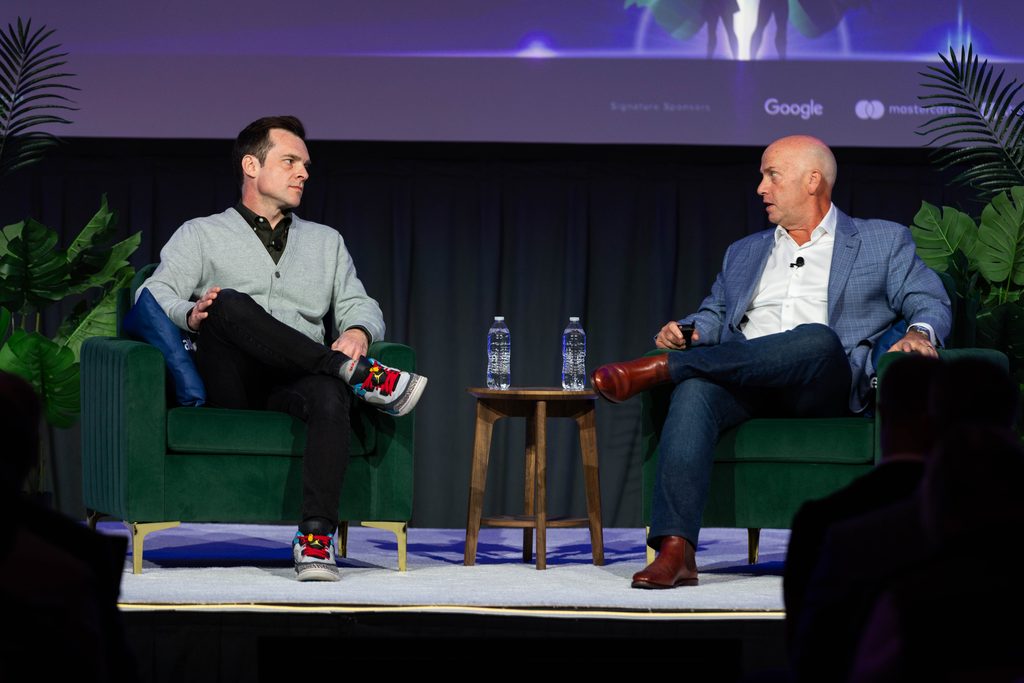
IMatt Charpentier leads identity at JPMorgan Chase and said the bank uses passkeys for login and customer authentication. He brought lessons from his time at Visa, where his team deployed passkeys to authenticate payments. Passwords have always been a pain point, he said, and customers are especially sensitive when it comes to their money. Passkeys give them a better alternative to passwords, which he called “a massive step change in how we do things.”
“Customer behavior will change almost overnight if the customer experience is good, if the value proposition is there, and if it’s easy to use and we’ve seen that with passkeys,” he said.
Looking forward he has concerns about AI agents. Charpentier wants verifiable credentials to delegate limited permissions to agents, along with one industry standard rather than a pile of competing specs.
“We now have machines that are anonymous acting on behalf of humans without a trust layer in the middle,” he said. “It’s a disaster, but it’s a solvable disaster.”
Keynote: Microsoft’s Pam Dingle is Looking to the Stars
Microsoft’s Pam Dingle closed day one with a talk built around the night sky. Her point was that security teams are hunting for signals in a lot of noise. Password attacks are falling, which she called a win worth taking. Token theft and adversary-in-the-middle phishing are rising, and exploit times keep shrinking.
The bigger challenge is AI agents. Identity pros spent 25 years building practices around systems and users. Agents arrived as a story nobody in the room wrote, and few attendees felt they could define one. Dingle made it clear that no one will hand over the answers. “This is our job. It’s not going to be handed to us. We get to craft it, and that is something that every single person here needs to internalize, in my opinion.”
Her starting points were practical. Identify agents, manage their full life cycle and limit what they can do. She warned that credential harvesting for agents could become a bigger debt than the MFA rollout.
“We need to build our picture, not just the tiny details, but how everything moves into a story,” Dingle said. “I believe that we can all find these patterns and do it together.”
Get Ready for Day 2
Day 2 will have even more great content across multiple tracks, with no shortage of sessions about passkeys in practice, security and regulatory discussions alongside technical insights for implementation.[
Not registered? Don’t miss out! Attend remotely and access all previous sessions on demand, and attend day 2 and 3 live via the remote attendee platform! See the full agenda and register now at authenticatecon.com.